

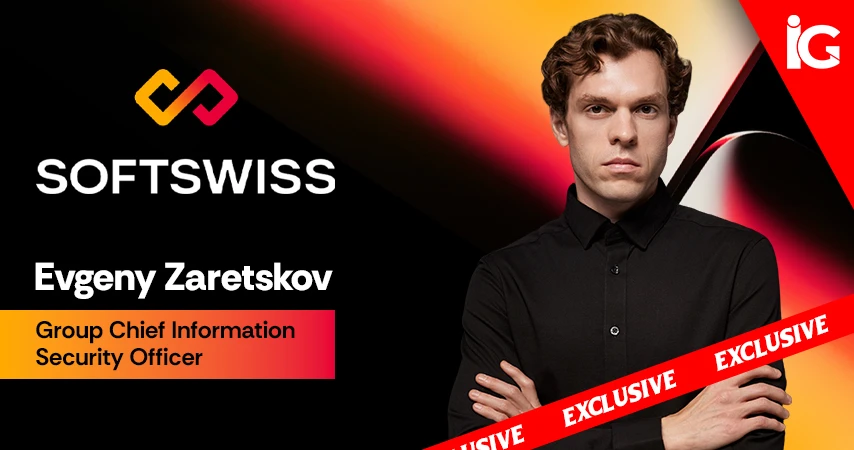
Exclusive: Why Modern iGaming Security Is About Trust, Not Just Protection, Says SOFTSWISS CISO Evgeny Zaretskov

Cybersecurity in iGaming has evolved far beyond traditional perimeter defense. Real-money transactions, always-on operations, complex technology ecosystems, AI-driven threats, and growing regulatory expectations are forcing operators and technology providers to rethink how security is designed, managed, and measured.
In this exclusive interview with iGaming News Today, Evgeny Zaretskov, Group Chief Information Security Officer (CISO) at SOFTSWISS, reflects on his journey across banking, e-commerce, and iGaming and shares his perspective on cybersecurity leadership, identity risk, security by design, AI governance, international security teams, and the trends that will shape the future of global iGaming security.
1. You’ve worked across banking, e-commerce, and now iGaming. Looking back, how have those experiences shaped your approach to cybersecurity leadership?
Evgeny:
The banking environment taught me control. E-commerce taught me scale. And iGaming taught me that you need both in real time.
In banking, you learn very quickly that you are protecting money, identity and trust under strict regulatory expectations. In e-commerce, security has to work at an enormous scale without making the customer experience unusable. iGaming brings those pressures together: real-money transactions, 24/7 operations, high traffic and increasingly complex regulation across markets.
That is why I don’t see security as a separate control function. A security leader has to understand what the business is trying to achieve, where the real risks are, and how to make the safer path the easier path. Product, engineering, operations and security should share responsibility for the outcome. If everything still has to come back to the security team for approval, you have created a bottleneck rather than a mature security model.
2. Cyber threats continue to evolve at a rapid pace. What do you believe are the biggest cybersecurity challenges facing the iGaming industry today?
Evgeny:
One of the biggest challenges is that cybercrime, fraud and identity abuse are becoming much harder to separate.
Attackers do not necessarily need to break the platform if they can convince the platform that they are someone else. Stolen employee sessions, infostealer credentials, social engineering, fake identities and increasingly convincing AI-generated content can all provide a route into systems or transactions. In an industry where money moves in real time, the time between an identity compromise and a financial loss can be very short.
The second issue is ecosystem risk. Operators depend on payment providers, game suppliers, cloud services and many other integrations. One compromised identity or third party can create exposure well beyond a single system.
So the challenge is no longer simply keeping attackers outside. It is knowing who and what to trust inside a highly connected environment – and detecting quickly when that trust is being abused.
3. You’ve often spoken about making security part of product development from the very beginning. Why is a “security by design” approach becoming so important for technology companies?
Evgeny:
Late security is expensive security.
If you discover a serious problem after a product has already been built, the business usually faces three bad options: delay the release, accept the risk, or rework the product under pressure. Security by design is about avoiding that situation.
When security requirements, safe defaults, testing and automated controls are built into the delivery process, teams know the boundaries before they reach production. That can actually increase delivery speed because developers are not repeatedly stopping for late security reviews or rebuilding something that should have been designed differently from the start.
There is another benefit that matters increasingly in regulated markets: evidence. If security is part of the development lifecycle, you can demonstrate how risks are identified and managed rather than trying to reconstruct the story before an audit or after an incident.
Security by design is not about putting more gates in front of developers. It is about needing fewer gates because the right controls are already part of how the product is built.
4. AI is transforming both cybersecurity and cybercrime. How do you see AI changing the way organisations defend against threats over the next few years?
Evgeny:
AI’s biggest impact on cybersecurity will be time.
Security teams already deal with more alerts, vulnerabilities and telemetry than people can realistically process by hand. AI can help correlate signals, prioritise what is actually dangerous, investigate suspicious behaviour and automate parts of containment much faster than a traditional queue-based model.
I don’t think that means replacing security analysts. It changes the division of labour. Machines will take on more of the continuous, high-volume work, while people concentrate on judgment, architecture, adversarial thinking, and decisions with significant business consequences.
Attackers get the same advantage, of course. Reconnaissance becomes faster, social engineering more convincing and malicious tools more adaptive. So the real advantage will not come from simply having AI. It will come from combining good telemetry, automation and clear decision rights well enough to respond at machine speed without giving up human control.
5. As more companies adopt AI tools, what steps should organisations take to ensure they use AI securely and responsibly?
Evgeny:
The first rule is to govern what AI is allowed to do, not only which model you allow people to use.
A tool that helps someone draft an email and an AI agent that can access production data, modify infrastructure or trigger a financial action are completely different risk classes, even if the underlying model is the same.
Organisations first need visibility: which AI systems are being used, what data they can access and what actions they are authorised to take. From there, the familiar security principles still work – strong identity, least privilege, data boundaries, logging and explicit approval points for high-impact actions.
AI systems also need continuous testing, particularly where they interact with external data or tools. Prompt injection, data leakage and abuse of an agent’s permissions have to be treated as real attack scenarios.
And human accountability must remain clear. AI may recommend or execute an action, but the organisation still owns the consequence.
6. You’ve built and led large international security teams. What qualities do you believe define an effective cybersecurity leader today?
Evgeny:
Three things matter most: judgment, translation and trust.
Judgement is knowing which risks genuinely matter to the business and being prepared to make decisions when the information is incomplete.
Translation is being able to explain those risks in terms of product, revenue, operations and regulation rather than expecting everyone else to become a security specialist.
Trust is just as important inside the team. A strong security organisation cannot rely on the CISO making every decision. You need specialists who understand the wider context, challenge assumptions, take ownership and are comfortable surfacing problems early rather than hiding them.
The best security leader is not necessarily the strongest technical expert in every room. The job is to build an organisation in which good security decisions can be made without you being in every room.
And while there are moments when security has to say no, most of the job is finding a safer way to say yes.
7. Looking toward 2027 and beyond, what trends do you believe will have the greatest impact on cybersecurity in the global iGaming industry?
Evgeny:
I would watch four shifts.
First, AI agents will start doing more real operational work. That turns AI security into an identity and authority problem: what can a machine access, what can it change, and who is accountable when it acts?
Second, identity and transaction integrity will become even more important. Deepfakes, stolen sessions and synthetic identities will make it harder to distinguish a legitimate user or employee from a convincing imitation.
Third, I expect operators and regulators to demand more continuous evidence of resilience from technology providers. Annual audits will remain important, but they cannot fully describe the security of systems that change every day.
And finally, supply-chain risk will keep growing because iGaming is an ecosystem of operators, platforms, payment providers, game studios, cloud services and other connected partners.
By 2027, having controls will not be enough. The strongest companies will be those that can continuously demonstrate that those controls are working.
About SOFTSWISS
SOFTSWISS is an international technology company providing software solutions for the iGaming industry, including online casino platforms, sportsbook technology, game aggregation, managed services, and payment solutions. Founded in 2009, the company serves operators across multiple regulated markets and focuses on secure, scalable, and innovative technology for online gaming businesses.