

Exclusive: Sal Debs on Why Compliance Must Move From “No” to Finding the Path to “Yes”

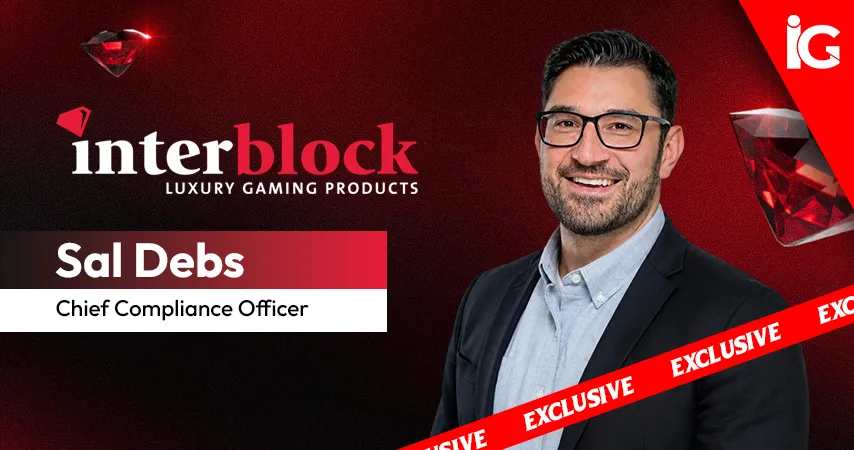
In this exclusive interview with iGaming News Today, Sal Debs, Chief Compliance Officer – Global at Interblock Gaming, explains why compliance needs to be involved at the beginning of projects rather than arriving at the end to reject decisions that have already been made. He discusses the challenges created by fragmented regulation, the importance of risk-based AML programmes and why compliance teams need to understand both business operations and technology.
Debs also explores the growing role of AI and automation, arguing that these technologies can remove repetitive work and allow compliance professionals to focus more on investigations, judgment and strategy. At the same time, he warns that the growing use of AI makes strong governance, data protection and accountability increasingly important.
Q1. You have worked on both the regulatory and industry sides of gaming. How has that experience changed the way you approach compliance today?
Sal Debs:
Working on both sides has fundamentally changed the way I look at compliance. From the regulatory side, the main focus is the integrity of the industry and making sure controls are actually protecting the public and the gaming environment as a whole. That has always been the lens through which I have viewed compliance.
On the industry side, particularly now working with Interblock on the manufacturing and supplier side, you also have to understand how regulatory requirements translate into actual products, systems and processes, and how those requirements affect business decisions.
The combination of both perspectives has taught me that compliance cannot operate in a vacuum. You need to understand regulation, but you also need to understand the business and, importantly, technology and how technology affects the business.
I also don’t believe compliance should come into a project at the very end and simply say, “You can’t do that.” Compliance needs to be involved from the beginning so that we understand what the business is trying to accomplish and can help design a compliant way to achieve it.
My philosophy is that compliance should not be the department that says “no” the most. It should be the department that helps the business find the path to “yes.”
Q2. Gaming regulation continues to evolve across different jurisdictions. What is the biggest challenge companies face when trying to keep up with changing expectations?
Sal Debs:
One of the biggest challenges is the combination of regulatory fragmentation and the speed at which the industry is changing.
Gaming is inherently jurisdictional. Every jurisdiction has its own requirements, and there is not necessarily one standard that applies everywhere. A product or process that is acceptable in one market may not be acceptable in another. There may be additional controls, approvals or requirements that need to be considered.
When you operate globally, as Interblock does, you cannot simply build one compliance framework and assume it will work everywhere. You need to be able to adapt.
At the same time, technology is developing extremely quickly. We are seeing new technology within products, payment technologies, AI, AI governance and data analytics. Companies are collecting more data and increasingly using that data to support business decisions.
The key, in my view, is to build an organization that can anticipate regulatory change rather than simply react to it. The industry is changing very quickly, and the ability to anticipate those changes can put a company ahead.
Q3. AML remains a major focus for gaming. How can companies make their AML programmes more effective while keeping the customer journey as smooth as possible?
Sal Debs:
For me, it is all about taking a risk-based approach.
Not every customer presents the same level of risk, and not every transaction presents the same level of risk. The approach needs to be situational and should focus the greatest level of scrutiny and resources where the greatest risk exists.
AI and technology can help significantly, particularly with routine and repetitive tasks. Better data and transaction monitoring can make AML processes much more effective. When I worked on the operator side, we relied heavily on technology because it allowed us to move away from very manual AML processes.
However, you still need people to evaluate the technology and make sure the information is coming through correctly. You need to understand the risk associated with a particular customer, transaction or vendor and make appropriate judgment calls.
So I think the combination is important: a proper risk assessment, effective systems, escalation processes and human judgment, supported by technology.
The objective should be to reduce risk while avoiding unnecessary friction for customers who do not present the same level of risk.
Q4. You have worked extensively across compliance, audit and risk management. What does it take to make risk management part of everyday business decisions rather than something discussed only when there is a problem?
Sal Debs:
It starts with culture. Risk management needs to become part of the broader business conversation rather than something that belongs exclusively to compliance or audit.
The hardest part is getting buy-in from the top. If senior executives understand the importance of risk management and support it, it becomes much easier for compliance, audit and risk teams to do their jobs.
The business is already making risk decisions every day. The question is whether those decisions are being made consciously and with the right information.
Compliance and risk teams also need to be accessible to the business and embedded within it. People should not only contact compliance when they believe they are about to get into trouble. By that point, you have already lost an opportunity to act proactively.
I want business teams to see compliance and risk as partners and support functions, not as departments that simply tell them what they cannot do.
Sometimes compliance does need to have a difficult conversation, but a good partner will also try to find a way to get the business to the right answer while remaining compliant.
Risk management should therefore be part of how a decision is made, not something that happens after the decision has already been made.
Q5. Where do you think AI and automation will make the biggest difference to compliance over the next few years?
Sal Debs:
AI and automation are going to have a huge impact, particularly because compliance teams deal with enormous amounts of information.
AI can help identify anomalies, prioritize investigations, analyse transactions and, importantly, monitor regulatory changes. Regulatory research and keeping up with constantly changing requirements can be extremely time-consuming, so this is an area where AI can provide significant value.
I see AI as being particularly useful for the mundane and repetitive work that takes up a lot of compliance resources.
But I don’t see AI replacing compliance professionals. I see it changing where they spend their time. If technology can take away lower-value repetitive analysis, compliance professionals can spend more time on judgment, investigations, strategy and actually solving problems for the business.
At the same time, the more we rely on technology to support decisions, the more important AI governance becomes. Companies need to understand the data, methodology and assumptions behind the outputs they receive.
There are still not enough AI governance programmes, AI committees or AI policies in place across companies. I think getting ahead of that is extremely important.
Q6. As a global Chief Compliance Officer, you work with regulators, senior executives and teams across the business. When commercial and compliance priorities don’t immediately align, what makes an effective compliance leader?
Sal Debs:
For me, there are three things that are critical: credibility, business understanding and communication.
First is credibility. You have to know the regulatory environment and be an expert in your field. Regulators and your own organization need to be able to trust that you understand the subject. You may not always have the answer immediately, but you need to know where to find it.
Second is understanding the business. You have to understand how the company operates from beginning to end. At Interblock, product compliance is very important, but it is not the only aspect of the business. Without understanding the business as a whole, it is very difficult to provide practical compliance advice.
The third, and perhaps most important, is communication.
Compliance leaders need to be able to take complex regulatory requirements and translate them into something that engineers, product teams, finance, operations and executives can actually understand and act upon.
Working on both the regulatory and industry sides has also taught me that understanding regulatory intent is extremely important. It is not enough to simply understand what the regulation says. You need to understand what the regulator is actually trying to achieve and why.
My experience at the Nevada Gaming Control Board helped me understand that intent, and I believe it has helped me in my subsequent roles.
Ultimately, I see three types of credibility as essential for compliance leaders: regulatory credibility, business credibility and technical credibility.
Q7. Looking toward 2027 and beyond, which regulatory or compliance issues should the gaming industry start paying much more attention to today?
Sal Debs:
I think there are several important trends.
First, I expect to see continued regulatory cooperation and information sharing across jurisdictions. That does not necessarily mean every jurisdiction will introduce identical regulations, but regulators are increasingly looking at common risks and sharing information. I think that will become increasingly important.
Second, I expect much greater scrutiny of technology itself as gaming becomes more technology-driven. Regulators will want greater assurance that systems, algorithms and data are functioning as intended.
I would expect compliance and audit functions to increasingly be required to produce reports or provide assurance around the systems and technologies being used. We could therefore see more audits focused specifically on technology.
Third, AI governance is going to become a major compliance issue. It is not only about how companies use AI, but also how they validate it, monitor it and establish accountability around it.
Companies need proper AI governance policies and procedures. They also need to think carefully about data protection when using AI tools. For example, companies should be cautious about putting confidential information into public AI tools rather than using enterprise solutions that provide appropriate data protection.
Overall, I think compliance is moving upstream. Instead of simply reviewing what the business has already built, compliance should increasingly help determine how the business builds things in the first place.
About Interblock Gaming
Interblock is a global gaming technology and manufacturing company focused on electronic table gaming and casino solutions. The company develops and supplies products designed for casino environments, combining gaming hardware, software and technology to support modern gaming floors.
Its portfolio and technology are used across international gaming markets, requiring the business to operate within a wide range of regulatory and compliance environments. This makes regulatory compliance, product standards, technology controls and risk management important elements of its global operations.